This cyber security analyst CV template shows a move from IT support into an in-house security operations team. The Word example connects alert investigation, vulnerability follow-up and detection improvements with practical results. The guide explains how to present experience for SOC, broader cyber analyst and governance-focused vacancies, including a first role in security.
Filename: FreeCVDownload_Cyber_Security_Analyst.docx
Content of this CV template
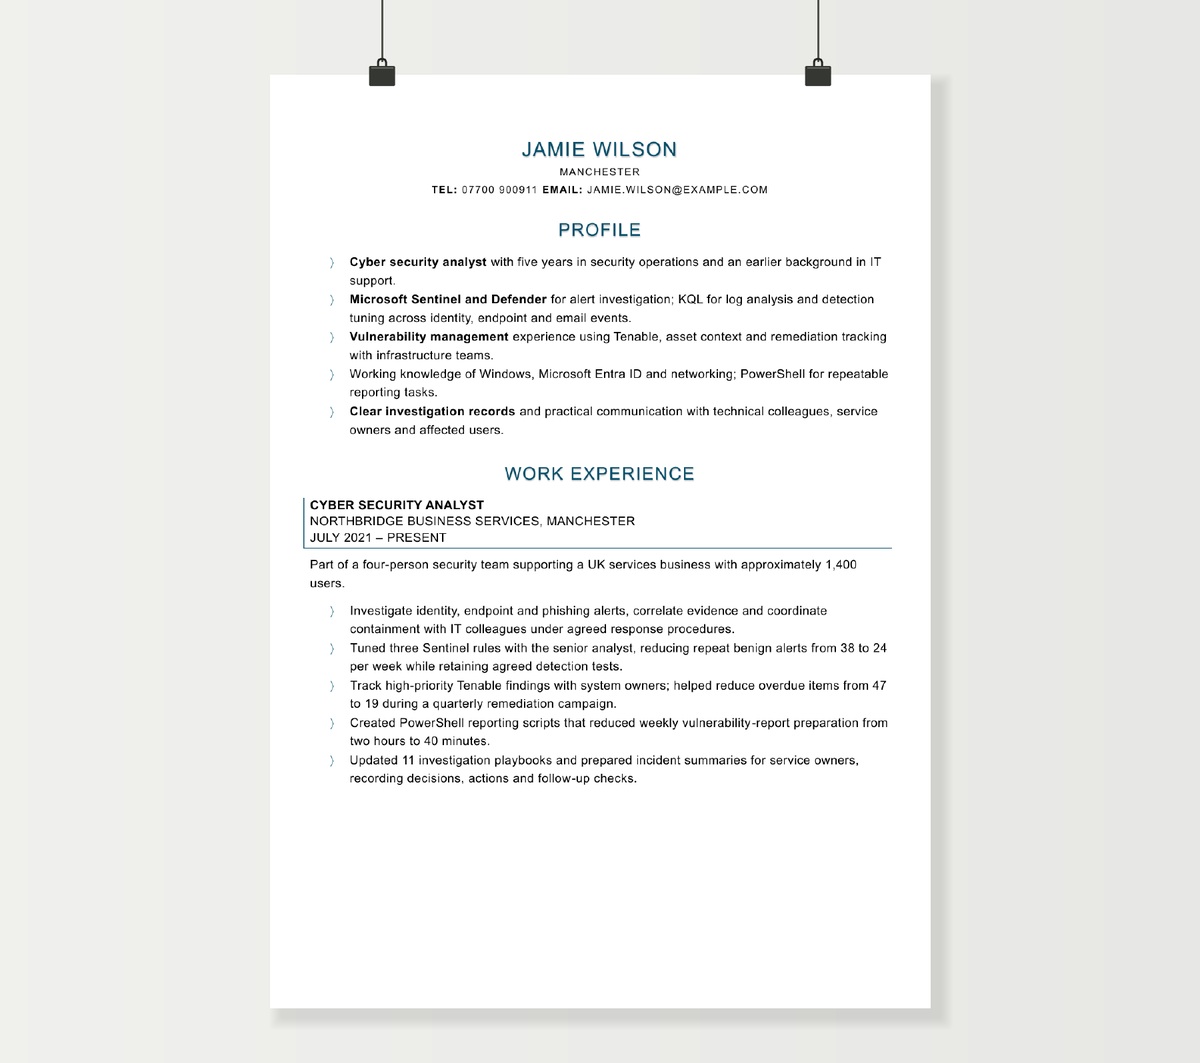
JAMIE WILSON
MANCHESTER
tel: 07700 900911 email: [email protected]
PROFILE
- Cyber security analyst with five years in security operations and an earlier background in IT support.
- Microsoft Sentinel and Defender for alert investigation; KQL for log analysis and detection tuning across identity, endpoint and email events.
- Vulnerability management experience using Tenable, asset context and remediation tracking with infrastructure teams.
- Working knowledge of Windows, Microsoft Entra ID and networking; PowerShell for repeatable reporting tasks.
- Clear investigation records and practical communication with technical colleagues, service owners and affected users.
WORK EXPERIENCE
CYBER SECURITY ANALYST
NORTHBRIDGE BUSINESS SERVICES, MANCHESTER
JULY 2021 – PRESENT
Part of a four-person security team supporting a UK services business with approximately 1,400 users.
- Investigate identity, endpoint and phishing alerts, correlate evidence and coordinate containment with IT colleagues under agreed response procedures.
- Tuned three Sentinel rules with the senior analyst, reducing repeat benign alerts from 38 to 24 per week while retaining agreed detection tests.
- Track high-priority Tenable findings with system owners; helped reduce overdue items from 47 to 19 during a quarterly remediation campaign.
- Created PowerShell reporting scripts that reduced weekly vulnerability-report preparation from two hours to 40 minutes.
- Updated 11 investigation playbooks and prepared incident summaries for service owners, recording decisions, actions and follow-up checks.
IT SUPPORT ANALYST
CALDER OFFICE SOLUTIONS, MANCHESTER
SEPTEMBER 2018 – JUNE 2021
Supported 600 users across three offices, resolving Windows, Microsoft 365 and access-related incidents.
- Investigated account lockouts and suspicious-email reports, gathering logs and escalating security concerns with clear ticket notes.
- Maintained endpoint inventories and coordinated patch deployment checks with infrastructure colleagues.
- Reworked the joiner and leaver checklist, reducing access requests returned for missing details from 18 to six per month.
- Explained MFA enrolment and account-recovery steps to colleagues, and created service-desk knowledge articles.
QUALIFICATIONS & DEVELOPMENT
BSc (Hons) COMPUTING — 2:1
MANCHESTER METROPOLITAN UNIVERSITY — 2018
Final-year project: analysis of authentication logs to identify unusual account activity.
MICROSOFT CERTIFIED: SECURITY OPERATIONS ANALYST ASSOCIATE
AWARDED 2024; RENEWED 2026
CompTIA SECURITY+
AWARDED 2025
INTERESTS
Five-a-side football, cooking and building small apps for everyday tasks.
How to write a cyber security analyst CV
A cyber security analyst CV should show how you turn technical evidence into a useful security decision. The tools matter, but so do the questions you investigated, the actions you coordinated and the records you left for the next person. A hiring manager needs to understand both your technical depth and how you work within a wider security service.
Begin with the actual responsibilities in the vacancy. “Cyber security analyst” can mean alert monitoring and incident response, vulnerability management, or a broader combination of technical security, governance and customer assurance. Your CV will be stronger when its opening evidence matches that balance.
Make your security specialism visible near the top
Use the profile to establish your current level, principal area of work and relevant environment. For a SOC role, that might be several years investigating endpoint and identity alerts in a Microsoft environment. For a governance-focused position, it might be control assurance, risk assessment and audit evidence within a software business.
Follow with a compact selection of capabilities that your experience can explain. Organising them by work is useful: investigation and detection; vulnerability management; cloud and identity; reporting and automation. The reader can then find relevant technologies without having to interpret an undifferentiated list of products.
Describe the setting of each role as well. An in-house team supporting one organisation differs from a managed security service working across several customers. Mention the estate, customer mix, team size or operating pattern where it helps explain the breadth of your responsibilities.
Explain what you did with an alert
“Monitored SIEM alerts” says little about the level of analysis involved. A stronger description connects the event, the evidence you examined and the decision or action that followed. Relevant evidence might include endpoint activity, sign-in records, email telemetry, network logs or information from the affected user.
For example: “Investigated suspicious sign-ins by correlating identity and endpoint records, established the affected accounts and coordinated containment with the infrastructure team.” This gives the reader a practical picture of your contribution without needing the full incident narrative.
Make your place in the response clear. First-line triage and escalation, independent investigation, coordinating containment and commanding a major incident are distinct levels of responsibility. Use verbs that describe the work you performed, then show how that responsibility developed between roles.
Include what happened after the immediate response when it adds value: an investigation summary, a revised detection, a control improvement or a completed follow-up action. These details demonstrate that your work reached a useful conclusion.
Show the depth behind SIEM, EDR and cloud tools
A product name becomes more informative when attached to an activity. “Microsoft Sentinel: KQL investigation queries and analytics-rule tuning” shows different experience from “Microsoft Sentinel: triage against established playbooks”. The same principle applies to Splunk, QRadar and endpoint detection and response platforms.
Select the level of detail that matters to the vacancy. You might have correlated several log sources, adjusted a detection threshold, investigated an endpoint timeline, reviewed cloud activity or helped onboard a new data source. Put the most substantial work in an experience bullet, with the product names in a short skills section for easy scanning.
For cloud security, identify the environment and the evidence you used rather than listing every cloud provider. Identity events in Microsoft Entra ID, AWS audit logs and endpoint investigations demonstrate different experience. Readers applying from infrastructure roles may find the cloud engineer CV example useful for describing the underlying environment before bringing security work to the front.
Present detection improvements as tested changes
Detection tuning, threat hunting and automation deserve space when they were meaningful parts of your work. Describe the problem you were addressing, the change you made and the way the team assessed it. A rule that produced fewer repeated benign alerts is useful evidence when the CV also explains the review or testing behind the change.
In this example, Jamie’s result combines a weekly alert measure with retained detection tests. The point is the quality of the improvement: analysts gained a more useful queue while the team continued checking the intended detection behaviour.
For threat hunting, a concise account of the hypothesis, data examined and outcome works well. An outcome may be a new detection opportunity or a gap in available logging, as well as a confirmed incident. Explain what the team did with the finding. For automation, name the recurring task and its benefit, such as faster evidence collection, more consistent reports or fewer manual handovers.
Describe vulnerability work through to remediation
Scanning is one part of vulnerability management. A strong CV also shows how you helped prioritise findings and move them towards resolution. Include the factors you used to inform the work, such as exposure, asset importance, available threat information and the relevant remediation deadlines.
Clarify the relationship with infrastructure, application or cloud teams. You may have analysed the findings and tracked actions while system owners implemented the fixes. Alternatively, you may have carried out configuration or patching work yourself. Explaining that division makes your contribution easier to assess.
Useful results include overdue findings reduced during a defined campaign, better ownership of assets, remediation verified through follow-up checks or a more reliable reporting process. Pair a count or percentage with the estate and period it covers. This gives the reader a basis for understanding the result.
Give governance and assurance their own evidence
For a broad cyber analyst or information security role, technical investigations may sit alongside risk registers, policy updates, supplier reviews and audit preparation. Describe the output you produced and who used it. “Compiled evidence for an ISO 27001 control review and tracked agreed actions with service owners” is more useful than simply adding “ISO 27001” to a skills list.
Choose frameworks according to their application in your experience. MITRE ATT&CK might help explain detection coverage; ISO 27001 might relate to the organisation’s information security management system; Cyber Essentials might concern a particular assessment and its supporting work. Give each name a reason to be on the page.
If you prepared customer-facing security reports or contributed to bids, explain how you translated technical findings into clear answers or priorities. A CV can show commercial awareness through the way you supported a customer decision, an assurance request or the delivery of a service.
Use measures that reveal service improvement
Security achievements are often about better visibility, consistency or response rather than a dramatic financial saving. Choose measures that show a change you can explain. Useful possibilities include:
- Time needed to prepare an investigation pack or recurring report.
- Repeat benign alerts associated with a specific rule or use case.
- Completion of agreed remediation actions within a defined period.
- Coverage of relevant log sources or documented investigation procedures.
- Quality or completeness of case records and shift handovers.
- Outstanding audit or assurance actions brought to closure.
Give the starting point and scope where they help. “Reduced weekly report preparation from two hours to 40 minutes” is readily understood. For incident response measures, explain whether the figure concerns acknowledgement, triage, containment or full resolution. These are different stages, and the distinction helps a hiring manager compare your experience.
A well-described qualitative result can be just as strong. Resolving an unclear ownership problem, producing a decision-ready incident summary or improving a playbook after an investigation can demonstrate judgement without requiring a percentage.
Show communication as part of security delivery
Analysts regularly work with people who need a decision or an action rather than a technical narrative. Use an example of explaining the impact, agreeing the next step or keeping the right people informed. A service owner, an affected colleague and another analyst will each need different information.
Shift handovers and case notes are particularly relevant to operations roles. Explain how you recorded evidence, current status, outstanding actions and escalation decisions so work could continue reliably. Senior applicants can also describe incident coordination, mentoring and reviewing colleagues’ investigations.
Build a first security CV around relevant evidence
IT support, network administration and cloud operations can provide a strong foundation for a move into cyber security. Bring forward work involving account access, endpoint inventories, patching, suspicious-email reports, troubleshooting and clear escalation. Explain the security relevance through the task itself.
Students and career changers can use selected projects to demonstrate the same reasoning. A useful project entry identifies the question, environment, evidence examined, method and finding. For instance, an authentication-log project could explain how you investigated unusual sign-ins and evaluated the resulting alerts. Label the project context naturally, such as university project, home lab or placement.
A short portfolio can support the CV when it contains readable investigation write-ups, documented queries or a small automation project. Give one or two strong items a direct link and a brief description of what the reviewer will find. A project’s conclusion and explanation are generally more informative than a long list of completed exercises.
Keep qualifications relevant to the next role
List the full certification title, awarding organisation and current status or relevant dates. For example, the Microsoft Security Operations Analyst Associate certification is more clearly identified by its full title than by the exam code alone. A recent renewal can show that a role-based credential is current.
Choose emphasis according to the position: foundational security knowledge, a particular platform, incident response or assurance. A relevant degree, apprenticeship and practical experience can each provide evidence; the qualification section should complement the work described elsewhere.
For an experienced analyst, recent substantial development is usually more helpful than a catalogue of introductory courses. For an entry-level applicant, a relevant dissertation, placement or practical assessment may deserve a little more explanation. Keep the strongest evidence easy to find whichever Word CV layout you choose.
Cyber Security Analyst CV FAQs
Use a description at the level your organisation permits: the type of environment, incident category, your responsibility and the improvement that followed. An anonymised account-compromise investigation can show evidence analysis and coordination without naming a customer or exposing its systems. Your CV can also focus on approved aggregate service measures and general process improvements.
Where clearance is relevant, follow your sponsoring organisation’s guidance about how it may be described and provide the requested information through the employer’s recruitment process. Holding clearance and meeting the conditions to be considered for clearance are different positions. The new sponsor manages any required application or transfer; detailed vetting information belongs in that process.
It can provide supporting evidence when you explain a relevant piece of work, such as analysing logs, reconstructing activity or writing a clear investigation report. Choose exercises that connect with the advertised duties. A ranking or badge list on its own gives less insight into how you would investigate and communicate in a security team.
Describe your experience with the platform you know, including the log sources, investigation tasks and query work involved. That helps the employer assess the transferable skills. Any training or lab work on the requested platform can sit in a separate development or project entry, making the different contexts easy to understand.
Give each assignment its dates, employer or agency relationship and a concise scope. Where contracts were similar, vary the evidence to show what each added: a different environment, customer group, detection improvement or response responsibility. A clear sequence lets the reader see the breadth of your work without repeating the same alert-monitoring duties under every entry.
Yes, where they help establish the operating environment or are relevant to the vacancy. State whether you worked a staffed shift pattern or joined an on-call rota, and connect it with handovers, escalation or response responsibilities. This is especially useful when moving between a continuously staffed managed service and an in-house team.
Describe the change in responsibility within the role: moving from supervised triage to independent investigations, reviewing detections, coordinating remediation, mentoring new analysts or taking a lead during incidents. A short progression sentence followed by examples can make that development visible even when the employer retained a single analyst title.